The TRENDnet Baby Monitor Left Live Feeds On The Internet
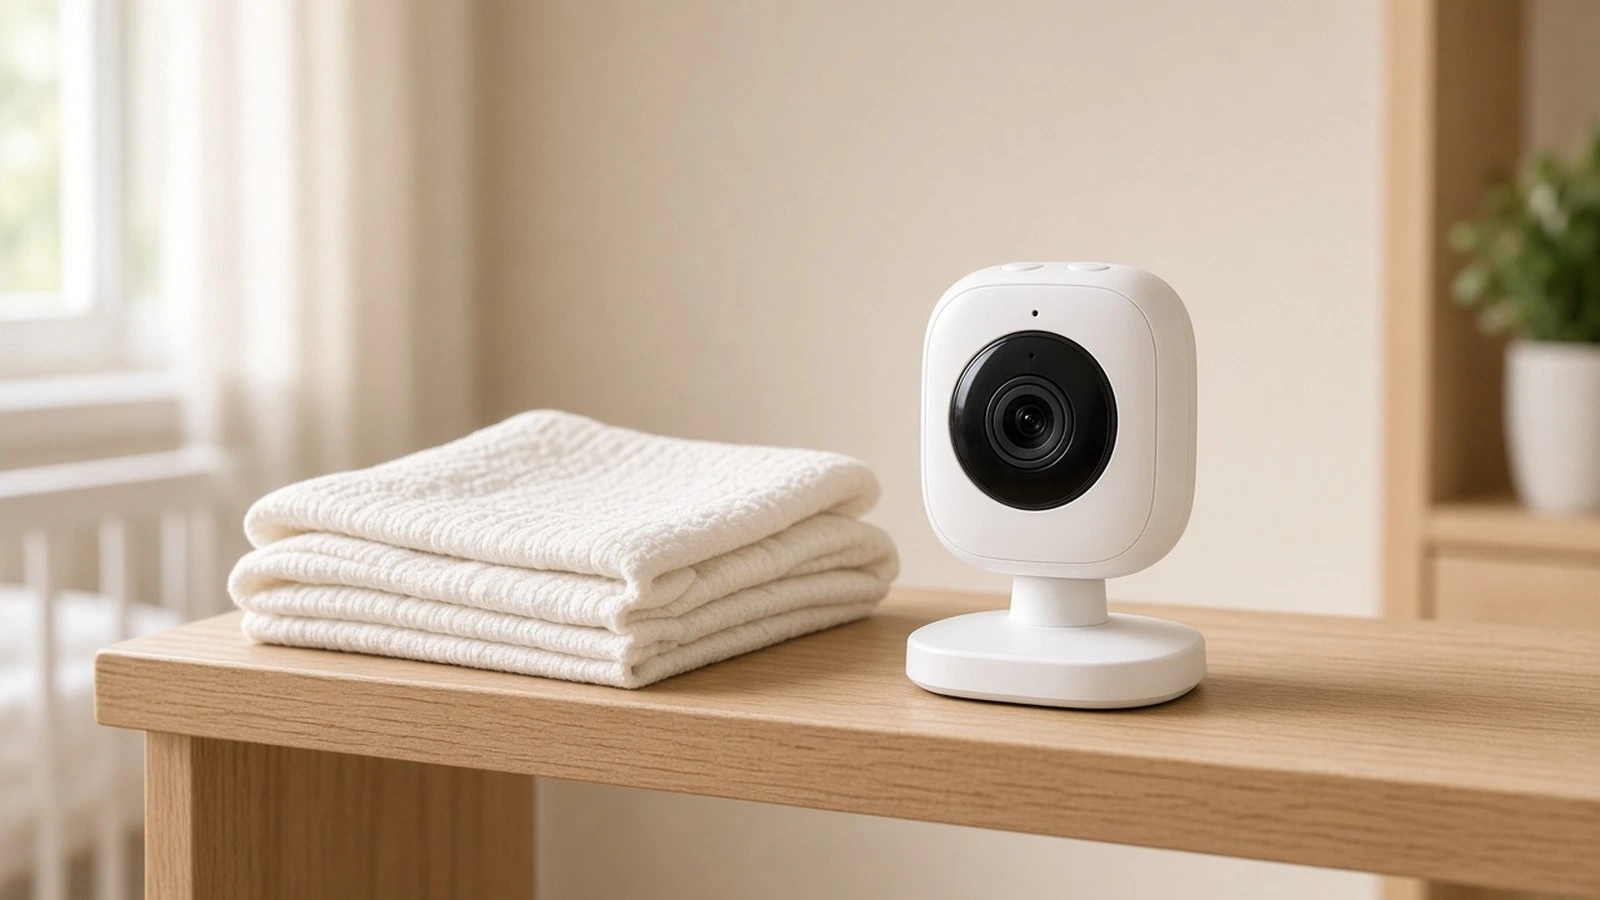
The FTC says the TRENDnet baby monitor, sold as secure, left live feeds public. Hackers posted links to nearly 700 cameras, including cribs.
Were TRENDnet baby monitor feeds public on the internet?
The FTC says yes. Faulty software left SecurView cameras open to anyone with the camera's internet address, and hackers posted links to nearly 700 live feeds, including babies in cribs.
The Federal Trade Commission says the TRENDnet baby monitor was sold as secure and then left on the open internet. SecurView cameras were marketed for home security and for watching a baby. Product descriptions called them secure. The software did not keep that promise. Anyone who had a camera's internet address could view the live feed, and in some instances listen. The September 2013 settlement announcement is the agency's first case against an everyday product that connects to the internet. The final order followed in February 2014.
Trust is a nursery whose only viewers are the people who live there. Security is a feed that has no public address. Incentive is a monitor that still shows the crib without paying a vendor to hold the picture. A SecurView baby camera that is reachable by internet address fails all three at once. The parents bought a window into their own room. Strangers received the same window.
Era 4 keeps the baby monitor and drops the path off the property. This page is the public record of what that path cost. The same pattern shows up in Ring home cameras and in Eufy no-cloud cameras.
What The TRENDnet Baby Monitor Actually Exposed
From at least April 2010, the FTC says, TRENDnet failed to use reasonable security in the design and testing of the software, including the setting that was supposed to require a password. Customers could believe they had turned protection on. The camera still answered anyone who knew where it lived on the internet.
In January 2012 a hacker exploited the flaw and published it. Hackers then posted links to the live feeds of nearly 700 cameras. The FTC says those feeds showed babies asleep in their cribs, young children playing, and adults going about their daily lives. Hundreds of households had their private camera feeds made public. The Electronic Frontier Foundation's privacy work describes the broader harm: a company that stores or routes the intimate record becomes the place a stranger reads it. Here the company did not even have to hand the file over. The address itself was enough.
TRENDnet uploaded a patch to its own website and tried to tell customers to visit that website and update. The fix lived where the vendor lived. A camera in a nursery that cannot fetch a patch on its own stays broken until the parent completes the vendor's errand.
Why A SecurView Baby Camera Was Reachable At All
A baby monitor has a small job. Show the crib to the person down the hall, and make a sound when the room does. The SecurView design added a third party: the internet address. Once the feed has a public address, every security claim is a claim about who may open that address. The password setting was supposed to be that claim. The FTC says the setting did not hold.
The Password On A SecurView Baby Camera Did Not Hold
The complaint's core fact is simple. The control customers used to require a password did not do what the label said. A household that chose "secure" still had a live picture that answered without credentials. NIST's Zero Trust guidance assumes a device will be reached by people who were never invited. A camera that skips the password has already skipped the only check it offered.
That is a different failure from a cloud login shared too widely. There was no account to revoke. The feed was a URL. Posting the URL was posting the baby.
Nearly 700 TRENDnet Baby Monitor Feeds Were Listed
"Nearly 700" is the FTC's number for the links hackers posted, not a guess about how many cameras were sold. Each link was a live feed. The pictures were ordinary home life, which is exactly why they were not meant for a public list. A crib at 2 a.m. is not a product demo.
The company had described the cameras as secure in numerous product descriptions. The February 2014 order bars that kind of claim when it is not true. TRENDnet may not misrepresent the security of the cameras, or the privacy of what they transmit, or how much control a consumer actually has over that information.
The Patch Still Sent The Parent Back To The Vendor
Once TRENDnet knew, the remedy was a file on the company website and a request that customers come get it. The order later required notice to affected customers, a website notice, and free telephone and email support for two years to help people update or uninstall. It also required a written security program and an outside assessment of that program every two years for the next 20 years.
Those are serious duties. They also describe a product that still depends on the vendor to become safe. A parent who never saw the notice still had the old camera on the dresser. Uninstall was a supported option because leaving it installed was not safe.
A TRENDnet Baby Monitor Never Takes A Public Address
The monitor is worth keeping. The public address is not. A camera whose only peer is the Home Computer has no internet address for a stranger to trade. The feed is a file in the house. The parent in the kitchen opens that file. A list on the internet has nothing to point at.
The Home Companion is the era built for this room. The Home Computer is the machine that holds the file. The Freedom Guide is the walkthrough for moving the household's records onto hardware the household holds.
The Crib Stays On The Home Computer
MATA Home sits in the house. A nursery camera that can call only that computer still shows the room. It does not register a feed that the rest of the internet can name. Listening, where the product has a microphone, stays on the same path. The Home Companion write-up already treats a baby monitor as a locked room. This FTC case is what an unlocked room looked like in public.
DLDeploy Is The Board For That Nursery Camera
DLDeploy is how a local ESP32 device is flashed and granted to the owner. We are building the direct integrations so that board can do its job by talking to the Home Computer, with no vendor account in the middle. A nursery camera on that path does not take a public internet address. The DLDeploy article is the product page. A camera that stays off the cloud is the firmware story beside it.
What The TRENDnet Baby Monitor Still Teaches
The order runs for years because the harm was structural. A camera marketed for a crib had a flaw from at least 2010, a public exploit in 2012, and a settlement that still had to beg owners to update or uninstall. The lesson for the next monitor is smaller than a 20-year audit program. Give the feed one address, inside the house, and the list of 700 links has nowhere to form.
FAQ
Short answers already in this article.
How many TRENDnet baby monitor feeds did hackers post?
The FTC says that after a hacker published the flaw in January 2012, hackers posted links to the live feeds of nearly 700 SecurView cameras.
What did the public TRENDnet baby monitor feeds show?
The FTC says the feeds showed babies asleep in their cribs, young children playing, and adults going about their daily lives. In some instances a stranger could listen as well as watch.
For how long had the SecurView baby camera flaw been in the product?
The FTC says that from at least April 2010, TRENDnet failed to use reasonable security on the cameras, including the setting that was supposed to require a password.
What did the 2014 TRENDnet order require for the baby monitor?
The February 2014 order requires a security program, outside assessments every two years for 20 years, notice to customers, and two years of free support to update or uninstall the cameras.
Can a nursery camera talk to the Home Computer instead?
A nursery camera flashed through DLDeploy is being built to talk only to the Home Computer. The feed is a file in the house. It does not take a public internet address.